

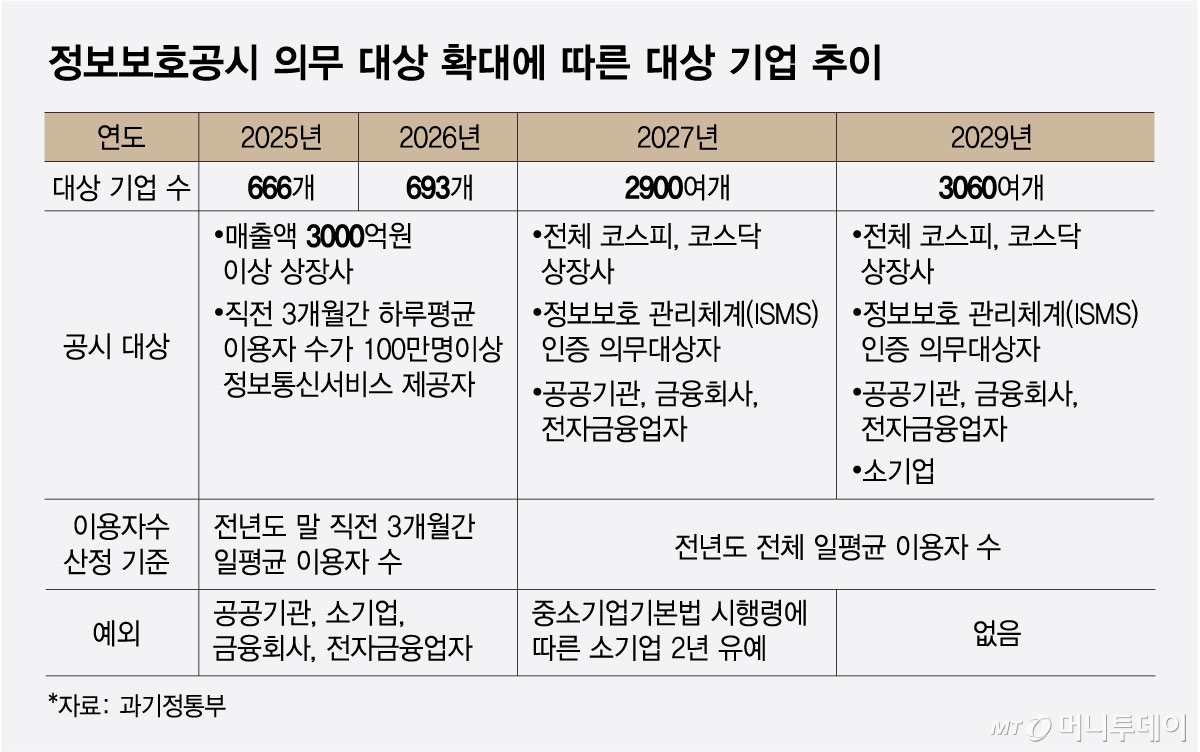
The government has expanded the obligation for information security disclosure, previously applied only to certain companies, to all listed firms. The move aims to boost investment and strengthen user protection by making companies' information security status public. As a result, information security disclosures are projected to quadruple starting in 2027. Voices are also emerging that institutional support, such as verification and sanctions, is necessary for this expansion.
The revised Enforcement Decree of the Act on Promotion of Information Security Industry, which passed the State Council meeting on the 20th, centers on expanding the scope of companies subject to mandatory information security disclosure to all listed firms. The obligation, currently applied to 693 entities including listed companies with annual revenue of 300 billion won or more and information and communication service providers with an average daily user base of 1 million or more, will be expanded to approximately 2,900 listed companies starting January 1 next year.
In effect, the vast majority of listed companies will have to disclose their information security levels, incident history, and details on information security organizations, personnel, and budgets. Only about 160 small and medium-sized enterprises were granted a two-year grace period.
The government plans to encourage companies to leverage information security investment not merely as a cost, but as a means of securing customer trust, through the expansion of disclosure obligations.
In fact, following the implementation of the mandatory information security disclosure system for companies with revenue of 300 billion won or more starting in 2022, their security investments have steadily increased from 1.5072 trillion won in 2022 to 1.8318 trillion won in 2023, 2.1196 trillion won in 2024, and 2.4230 trillion won in 2025.
However, given that information security disclosures are expected to surge by more than fourfold starting next year, weight is being placed on the opinion that verification is necessary. This is because there are no clear means of verifying false or negligent disclosures, and auxiliary measures are needed to guarantee the accuracy and reliability of disclosures.
The controversy over lenient sanctions, where failure to fulfill disclosure obligations results in fines of 10 million won or less, policies to alleviate the burden on small and medium-sized listed companies, and expanding user access to disclosures are also cited as challenges.
A Ministry of Science and ICT official stated, "We place significance on the fact that companies voluntarily make information security disclosures," while adding, "If disclosures are found to be negligent through subsequent verification, sanctions such as fines can be imposed."

 in TECH
