
The Ministry of Science and ICT has activated an emergency response system in response to recent consecutive personal information infringement (hacking) incidents in the financial sector.
On the 4th, the Ministry of Science and ICT announced that it has activated an emergency response system with the Korea Internet & Security Agency (KISA) regarding recent hacking incidents in the financial sector and is taking all-out measures to prevent the spread of similar incidents. Currently, investigations and responses to hacking incidents in the financial sector are being carried out centered on the Financial Services Commission, the Financial Supervisory Service, and the Financial Security Institute. Accordingly, the Ministry of Science and ICT and KISA have decided to strengthen threat response to prevent the spread of similar attacks to the private sector and additional damage.
The Ministry of Science and ICT and others strengthened the response system of the KISA Internet Security Center (KISC) so that they can quickly respond to the possibility of additional damage caused by hacking in the financial sector. The Ministry of Science and ICT explained, "We have activated an emergency response system by strengthening monitoring of major companies' homepages, reinforcing personnel for incident response, and keeping emergency dispatch teams on standby at all times."
Additionally, they guided institutional investors and companies to strengthen their own security measures by providing cyber threat information through systems such as Bogohana (Protect Korea) and cyber threat information analysis and sharing. They sent security inspection recommendation emails to approximately 28,000 companies registered with the CISO system. Regarding overseas attacker Internet Protocol (IP) addresses identified by the Financial Security Institute, they provided relevant threat information to the corresponding cloud service providers and requested necessary measures such as blocking malicious activities.
The Ministry of Science and ICT explained, "We are continuously sharing information with related institutional investors such as the Financial Services Commission, and we are preparing personnel and response systems in advance so that we can immediately deploy them to the scene if KISA or other specialized personnel support is requested by the Financial Services Commission, the Financial Supervisory Service, etc." and added, "We plan to continue close cooperation with related institutional investors during the incident investigation process as well."
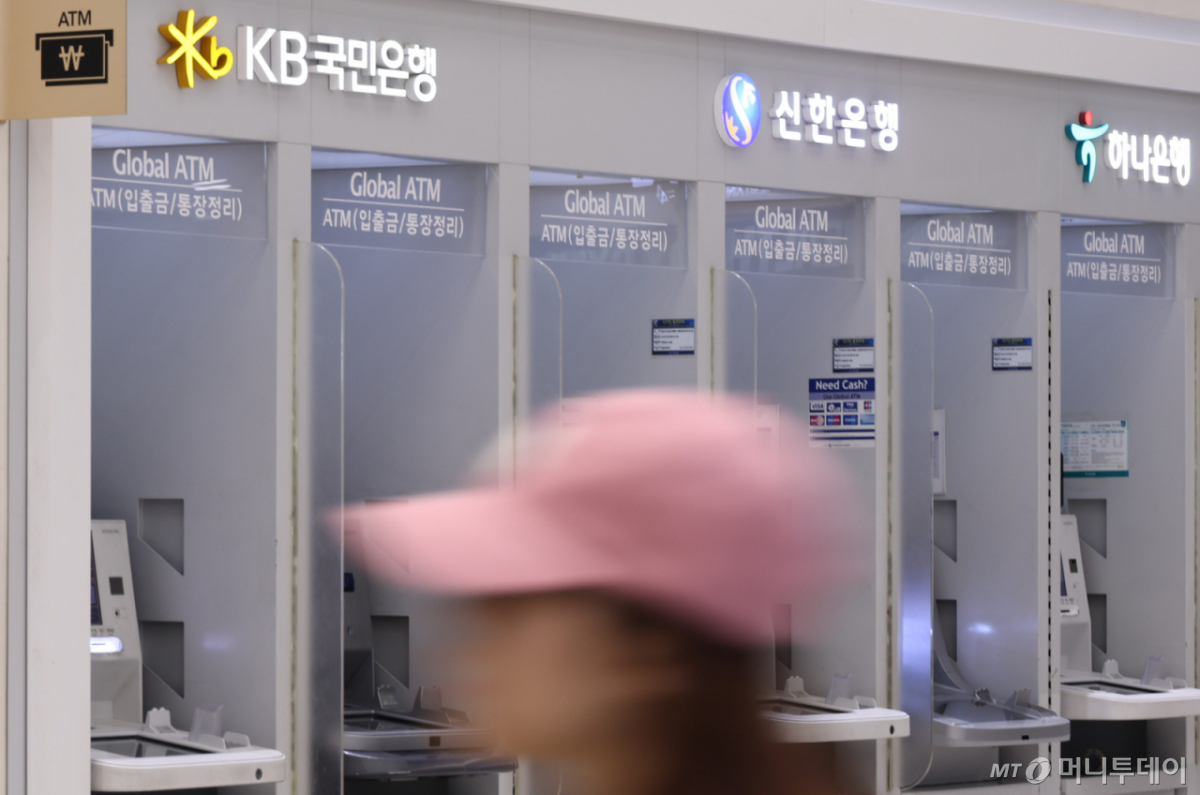
Meanwhile, starting with the leakage of personal information of approximately 25,000 customers at Shinhan Bank on the 1st, hacking incidents have occurred consecutively at seven financial institutions, including banks, savings banks, and capital companies: KB Kookmin Bank, Hana Bank, Busan Bank, Yegaram, Welcome Savings Bank, and Hyundai Capital. Amid reports of the possibility of simultaneous attacks exploiting AI (artificial intelligence), the Financial Services Commission held an "Emergency Inspection Meeting for the Entire Financial Sector" chaired by Lee Eok-won (Chairman) on the afternoon of that day, ordering measures to prevent similar incidents.
 in TECH
