

The Rural Development Administration has formulated a plan to file an administrative review against the Personal Information Protection Commission (PIPC)'s 168 million won surcharge.
The administration argues that it is unfair for the revised law to be applied retroactively to an already terminated outsourcing contract. It is assessed as unusual for one government agency to file an administrative review against another government agency.
Personal Information Protection Commission: "Rural Development Administration failed to fulfill management and supervision duties"
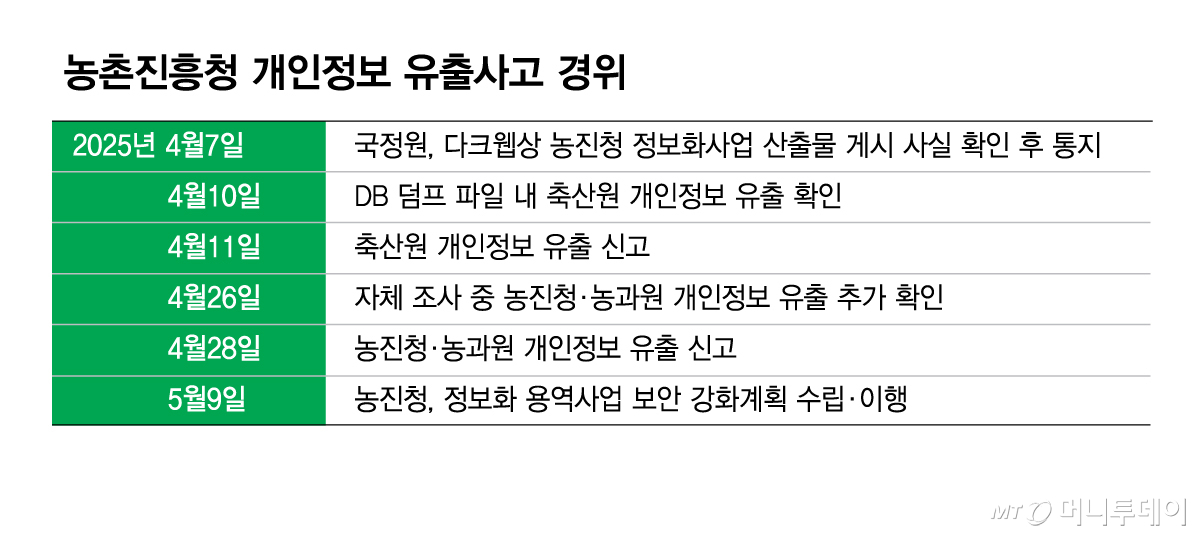
According to relevant ministries on the 26th, the Rural Development Administration formulated a plan with this content in mid-month. The PIPC resolved to impose a surcharge and issue corrective recommendations against the Rural Development Administration last May, and delivered the disposition on August 12. The Rural Development Administration can file an administrative review within 90 days from the date it became aware of the disposition.
In April last year, Misotech, an SI company that had signed an outsourcing contract with the Rural Development Administration, had personal information stored on a network-attached storage (NAS) device stolen by an unidentified hacker.
During this process, approximately 571,000 pieces of personal information, including names, contact details, and addresses contained in six types of personal information files such as homepage member information, were leaked.
The PIPC determined that the Rural Development Administration had not effectively fulfilled its duty to manage and supervise Misotech's personal information processing status. The commission emphasized in its resolution document that "administrative and public agencies have a duty to more closely manage and supervise outsourced companies."
First, the PIPC determined that the Rural Development Administration was unaware of the fact that Misotech had built and operated the NAS until the time of the breach incident.
The PIPC stated, "Although the Rural Development Administration conducted on-site security inspections, they were centered on information security, and since an average of 3.6 projects per day were inspected, it is difficult to regard them as effective inspections."
Furthermore, the Rural Development Administration only received a 'Certificate of Non-Possession of Data' from Misotech at the end of each service project, without inspecting or confirming whether personal information had been destroyed on laptops, external hard drives, etc. It was also pointed out that member information provided to Misotech while considering homepage integration was not retrieved and destroyed.
Rural Development Administration: "Outsourcing contract ended in 2022... Application of 2023 revised law is unfair"
The Rural Development Administration argues that the outsourcing contract with Misotech, the system maintenance company responsible for the personal information breach, was terminated on December 21, 2022. Accordingly, it claims that the application of the revised Personal Information Protection Act, which took effect on September 15, 2023, is unfair.
The revised Personal Information Protection Act stipulates that a surcharge can be imposed on the principal if the principal neglects management, supervision, and education, resulting in the outsourced company violating the Personal Information Protection Act. The principal's duty of management and supervision existed even before the revision, but the basis for imposing a surcharge was added with the implementation of the 2023 revised law.
However, the PIPC rejected the RDA's arguments on several grounds. First, the RDA had continued to sign annual outsourcing contracts with Miso Tech for other IT projects through this year, meaning it remained in a position to monitor and supervise the company. Second, under Supreme Court precedent, a violation involving failure to fulfill a legal duty to act continues until that duty is performed.
The commission therefore determined that the RDA's breach of its oversight obligations continued until May last year, when it drew up a plan to strengthen security. Third, the "data non-possession pledge" signed with another contractor, Saehan J Software, did not prove that the RDA's oversight obligations had ended.
A Rural Development Administration official stated, "In the same Misotech hacking case, affiliated agencies, the National Institute of Agricultural Science and the National Institute of Animal Science, received different dispositions." '
He added, "We are reviewing from multiple angles whether to file an administrative review for both the Rural Development Administration and its affiliated agencies, and we are not considering an administrative lawsuit."

 in TECH
