
As AI agent hacking attacks targeting the financial sector are becoming a reality, it was revealed that large banks' investments in AI-related security account for less than 1% of their total information technology (IT) budgets. Moreover, most of this budget is concentrated on detecting insider abnormal behavior, with half of the funds allocated to this area, leading to repeated criticism that monitoring systems designed to detect abnormal transactions from external IP addresses are being neglected.
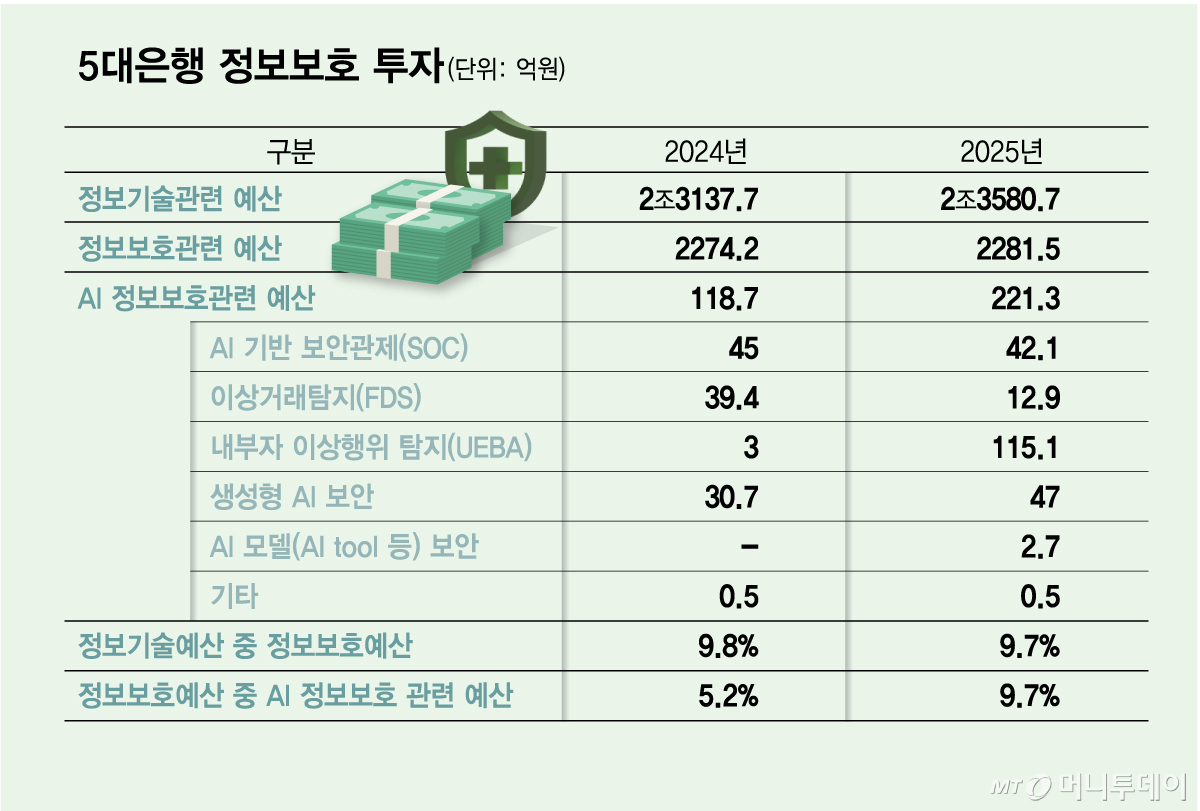
According to financial industry sources on the 11th, the IT-related budgets of the five major banks—KB Kookmin, Shinhan, Hana, Woori, and NH Nonghyup—as of the end of last year totaled 2.358 trillion won.
Of this amount, the information protection budget was 228.1 billion won, representing about 9.7% of IT-related budgets. Within that, investment related to AI security was 22.1 billion won, accounting for 9.7% of the information protection budget. The amount spent on AI security out of the total IT-related budget is roughly 0.9%.
By bank, Hana Bank had the highest proportion of AI security spending within its information protection expenditure at 23.3%. This was followed by KB Kookmin Bank at 11.5%, NH Nonghyup Bank at 4.5%, Woori Bank at 3.9%, and Shinhan Bank at 3.2%.
The financial sector tends to invest more in information protection compared to other industries, given that it handles sensitive personal information such as customer assets and credit data. However, unlike the scale of information protection investment, the construction of security systems utilizing AI can still be considered in its early stages. Since late last month, hacking incidents targeting financial companies, including Shinhan, KB Kookmin, Hana, and BNK Busan Bank, have occurred consecutively, with AI agents being identified as the masterminds. As external attackers successively infiltrated loan solicitor-exclusive services and business support systems used by employees, personal information of customers and staff was leaked, prompting financial authorities to launch emergency inspections.
A bigger issue lies in the composition of AI security investment. Among the five major banks' AI security investments, the area with the largest expenditure is User and Entity Behavior Analytics (UEBA), which detects insider abnormal behavior. The amount allocated here was 11.5 billion won, accounting for more than half—52%—of the total AI security investment budget. Generative AI security followed at 21%.
In contrast, relatively little investment has been made in systems that detect signs of external intrusion. The investment share for AI-based Security Operations Center (SOC) monitoring, which detects cyberattacks on internal servers or networks, was 19%. Fraud Detection Systems (FDS), which identify fraudulent transfers from customer accounts, accounted for only 5%. Even combined, these two areas make up less than one-quarter of the total AI security investment.
The method used in this hacking targeting the financial sector is presumed to be so-called "credential stuffing," where personal information posted on dark web sites is indiscriminately input to gain access. Consequently, the importance of monitoring external intrusions is increasing. As AI agents automate everything from vulnerability scanning and analysis to securing attack paths and executing actual attacks, the speed and scope of attacks are expanding daily.
Experts point out that even if AI agents have increased the speed of attacks, the methods themselves have existed for a long time, making external monitoring capabilities crucial for detecting and blocking abnormal access early. They explain that had real-time detection captured repeated login attempts, bulk information queries within short periods, or connections from abnormal IPs, the spread of damage could have been blocked more quickly. A security expert noted, "Intrusion attempts continued for over 10 hours, whether through back doors or front doors, and multiple information queries were made, yet measures such as IP blocking did not function, indicating that the fraud detection system was inadequate."
Abroad, there is also a trend of expanding AI security investment. According to IANS, a U.S. cybersecurity consulting institutional investor, software-related security, including AI-related investments, accounts for 35% of information protection budgets. Among 500 CISOs who participated in the survey, 69% responded that they plan to increase AI security spending next year.
Domestic banks are also expected to actively increase their AI security investment following this incident. This is particularly because the government continues to push for the relaxation of network separation regulations while strengthening its stance on building AI-based security systems. A bank official said, "It was necessary to lower network separation regulations to connect external security systems such as commercial miToss, and the companies selected in the first phase of network separation relaxation are pushing this forward, so going forward, we will focus on this aspect within network separation relaxation." The official added, "If guidelines for security personnel or budgets become stricter following this incident, it will be fully reflected in the budget starting next year."
 in FINANCE
