
The ripple effects of the AI (artificial intelligence) hacking crisis that began at commercial banks have reached the securities industry. Brokerages have stepped up security inspections by blocking suspicious IPs and activating a 24-hour emergency duty system. Traces of "scanning," in which hackers probe for vulnerabilities in security systems, were detected at some brokerages, but it has been confirmed that no damage such as actual system access or information leakage has occurred to date.
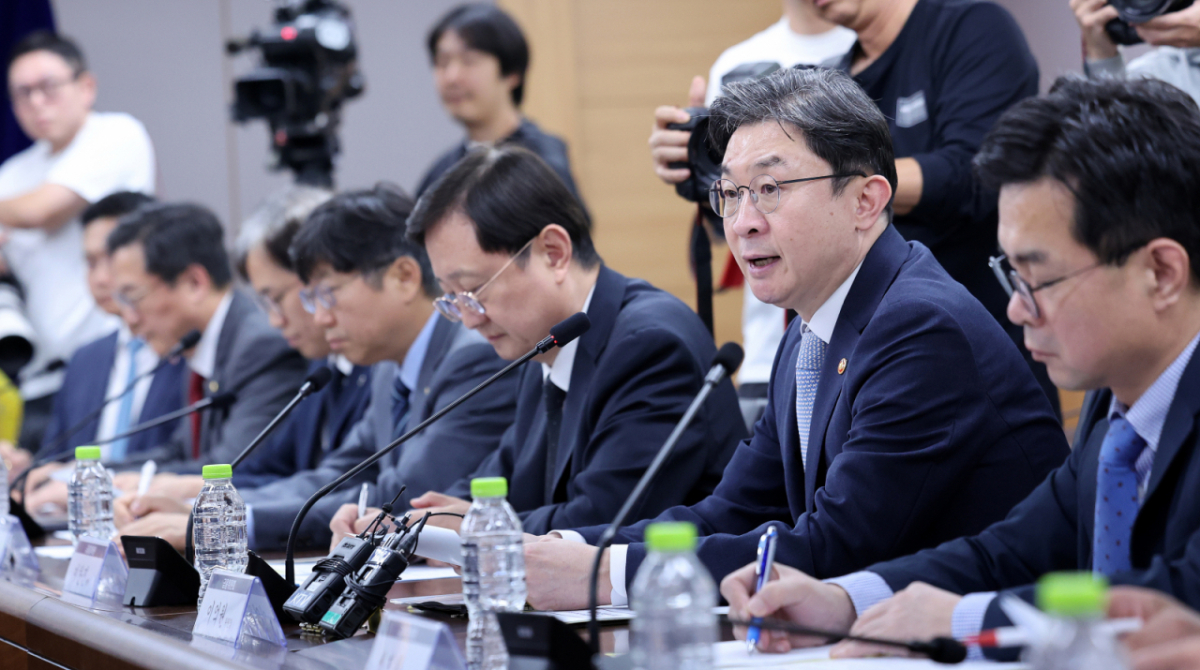
According to the financial investment industry on the 6th, no damage such as customer or employee information leakage caused by AI hacking was identified at the country's top 10 comprehensive financial investment businesses (Mirae Asset, Korea Investment, NH Investment, KB, Kiwoom, Shinhan Investment, Hana, Samsung, Meritz, and Daishin) and two fintech-based brokerages (Toss Securities and Kakao Pay Securities). While security personnel are communicating about the situation, it is known that no damage cases have been shared to date. Previously, financial regulators distributed a checklist containing 12 items to approximately 500 financial institutions, requesting them to verify whether attack IPs had been blocked and whether damage investigations were conducted. Brokerages must confirm compliance with emergency inspections by the 8th.
However, traces of scanning, which is the pre-hacking reconnaissance stage, were also discovered at one or two brokerages. Scanning is the initial stage where hackers check for security weaknesses before attempting system access. If hackers discover vulnerabilities during this stage, it can lead to system access, intrusion, and information leakage. However, it is assessed that the situation has remained at the scanning stage without leading to actual damage cases.
A senior official in the financial investment industry said, "Scanning corresponds to the front end of the hacking attack process," adding, "If vulnerabilities are discovered, hackers attempt actual access and then proceed to the stage of breaching security networks. What has been identified at some brokerages so far is only up to the preceding scanning stage."
Brokerages are raising their alert levels regardless of whether damage has occurred. In addition to activating emergency response systems during the Chuseok holiday (the 3-5), some are expanding the scope of inspections to the past year to check for any suspicious access in the past. In particular, brokerages affiliated with major financial holding companies that include commercial banks where intrusion incidents occurred have raised their response levels by forming separate task forces (TFs).
A Shinhan Investment Corp official said, "We are activating an emergency response team and strengthening night duty to enhance communication between emergency monitoring and internal IT personnel."
A KB Securities official stated, "As a result of in-depth analysis of system logs regarding recent financial sector hacking incidents, it has been confirmed that there is no evidence of hacking attempts or intrusion incidents related to this incident to date," adding, "We are immediately blocking threat IPs provided by the Financial Supervisory Service and the Korea Financial Security Institute, and continuously maintaining an enhanced security monitoring response system."
A Hana Securities official said, "As soon as we became aware of the commercial bank AI hacking crisis, we formed a related TF (task force) and blocked IPs identified as being used for hacking," adding, "We have completed inspections including past data and access history, and no separate traces of intrusion or abnormal signs have been confirmed to date."
Fintech-based brokerages, which focus on non-face-to-face and mobile services and have relatively many external touchpoints, have also stepped up monitoring. A Toss Securities official explained, "We completed proactive blocking and response measures based on information identified externally, and are continuously monitoring related trends through 24-hour security monitoring."
A Kakao Pay Securities official said, "In coordination with relevant institutional investors, we reflected the latest intrusion indicators in our security system and are operating with enhanced security monitoring."
 in STOCK
