

Following the banking sector, hacking incidents have occurred consecutively at securities firms, asset management companies, and virtual asset exchanges, heightening security concerns across the entire financial industry. As attack targets expand to include not only major financial transaction systems but also externally connected servers and general business systems, there are calls for financial institutions to strengthen their security management frameworks.
Daishin Securities: Information of 38,490 customers leaked…Mirae Asset Management and Upbit also affected by intrusion incidents
According to the financial investment industry on the 28th, it was confirmed that personal and credit information belonging to 38,490 customers had been leaked from Daishin Securities. On the 17th, Daishin Securities detected signs of abnormal external access on a server linked to non-face-to-face securities account opening for investment agency services.
Daishin Securities blocked internet protocol (IP) addresses used in the attack and reported the incident to relevant authorities. Subsequently, after analyzing approximately 60,000 signals disguised as normal service requests together with the Financial Security Institute, the company confirmed the customer information leak on the 26th.
The leaked information includes eight items: customer names, email addresses, residential addresses, communication IDs, bank names, deposit and withdrawal account numbers, Daishin Securities comprehensive account numbers, and mobile phone numbers. Some of this information, such as account numbers and mobile phone numbers, was encrypted. Daishin Securities stated that no unauthorized access to core business systems or signs of secondary damage have been confirmed to date.
Mirae Asset Management also recently confirmed that information had been leaked due to abnormal external IP access on some web systems. The company immediately blocked the access path and reported the incident to financial authorities, taking measures such as blocking via a Web Application Firewall (WAF) and suspending vulnerable functions.
It is currently understood that information related to general business systems was leaked, with no signs of direct intrusion into servers or databases. There are also no indications of leaks involving unique identification information such as resident registration numbers, sensitive information, or personal credit information. The company is investigating the cause and scope of impact with an external security specialist agency.
Virtual asset exchange Upbit also became aware on the 27th that personal information had been leaked due to unauthorized external access to its internal mobile groupware. Upbit has reported the incident to relevant agencies and is investigating the scale and scope of the leak. It has not yet been confirmed whether member information from the exchange was included.
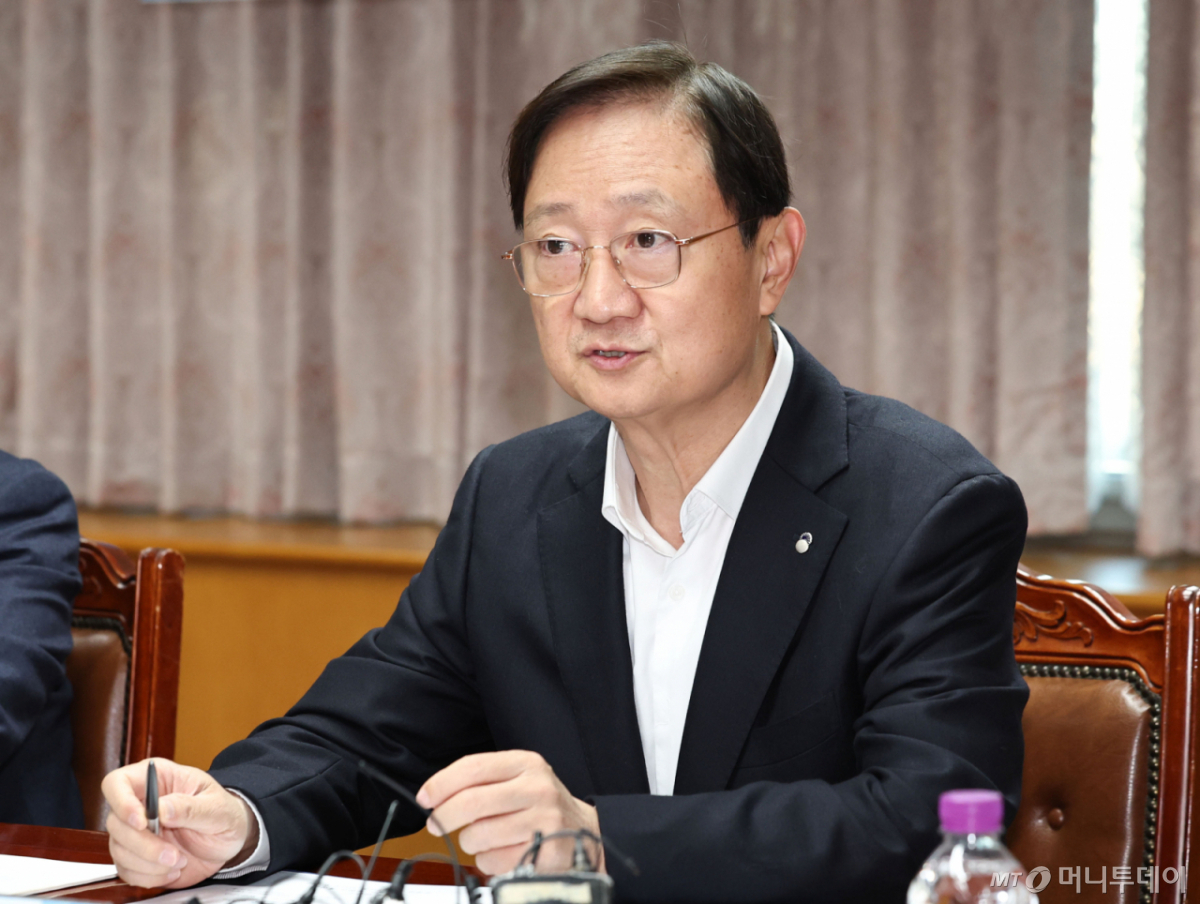
Lee Chan-jin, Governor of the Financial Supervisory Service: "Attacks expanding to non-core facilities"…Calls for strengthened security management
Financial authorities also expressed concern over the consecutive intrusion incidents. At a meeting with the chairs of the boards of directors of eight major bank holding companies on the 28th, Lee Chan-jin, Governor of the Financial Supervisory Service, stated, "I understand that a hacking incident has occurred overall at a major securities firm yesterday." The Governor diagnosed recent intrusion incidents at financial institutions by noting, "As cyberattack methods become increasingly sophisticated day by day, they are showing an all-encompassing trend, with targets expanding to non-core facilities."
The Governor warned of the possibility that hacking utilizing artificial intelligence (AI) could lead to the normalization of security vulnerability detection and simultaneous attacks, emphasizing that financial institutions must build autonomous defense systems capable of proactively identifying and eliminating vulnerabilities.
The Governor pointed out, "It is unacceptable for the practice of treating IT security as a secondary task and formally complying only with regulatory requirements, or perceiving IT security investment as a 'cost' and failing to allocate sufficient personnel and resources, to continue." He also stated that IT security is a core business essential for protecting customers' assets and information and maintaining financial trust, urging boards of directors to take the lead in strengthening security capabilities.
Concerns are growing within the financial sector over secondary damage resulting from personal information leaks. Even if actual monetary damage has not been confirmed, there are indications that leaked information could be exploited for phishing scams impersonating financial institutions, making it important to quickly assess the scope of damage and implement customer protection measures.

 in STOCK

