

Amid a surge in large-scale personal data breach incidents, an amended law raising fines to a maximum of 10% of sales from the current 3% will take effect. Companies that implement preventive measures such as advance investment may receive fine reductions of up to 40%. Additionally, the responsibilities of business owners and CEOs (chief executive officers) will be strengthened, along with the authority of CPOs (chief privacy officers).
The Personal Information Protection Commission announced on the 10th that the amended Personal Information Protection Act, which was promulgated on March 10, will take effect starting from the 11th. Key provisions include: imposing fines of up to 10% of total sales for repeated violations within three years due to intentional or gross negligence; causing large-scale harm affecting over 10 million people through intentional or gross negligence; and failing to comply with corrective orders, resulting in personal data breaches. Sales unrelated to the violation will be excluded from the calculation.
Specific fine calculations will be based on a comprehensive assessment of the nature, severity, and circumstances of the violation, as well as the scale of harm, followed by adjustments for aggravating or mitigating factors. Aggravation ratios have been increased: previously 15% for a single repeat offense and 30% for two or more; now set at 20% for one repeat, 40% for two repeats, and 80% for three or more repeats. Additionally, failure to report or notify within the statutory deadline, or failure to take measures such as warnings to prevent further harm, will result in an additional aggravation of up to 30%, encouraging proactive prevention and rapid response.
Companies that strengthen their protection systems through advance investment may receive a reduction of up to 40% from the base fine amount, except in cases involving intentional or gross negligence. Criteria for this reduction include: the scale, proportion, continuity, and degree of increase in investments such as budget, personnel, facilities, and equipment; the level of personal data protection systems managed by CEOs, CPOs, and specialized personnel; and additional efforts beyond statutory obligations.
Furthermore, to enhance proportionality, an additional reduction of up to 50% may be applied based on the specific nature, severity, scale of harm, and impact of the violation. However, fine reduction ratios have been lowered: from a maximum of 50% for obtaining ISMS-P certification to 30%; from 40% for implementing self-regulatory codes to 20%; and from 30% for protection level assessments to 15%. Major public institutions will no longer receive reductions based on their operational form or scale, thereby strengthening accountability.
The amended law explicitly establishes the ultimate responsibility of business owners and CEOs, while adding duties for CPOs such as managing specialized personnel, securing budgets, and reporting to the board of directors. It also mandates that any designation, change, or removal of a CPO must be approved by the board of directors and reported to the Personal Information Protection Commission.
To strengthen remedies for victims, new measures include: introducing a notification system for potential data breaches; expanding breach notification items (e.g., applications for dispute mediation and methods for claiming damages); and adding categories for reporting or notifying breaches involving forgery, alteration, or destruction of personal information.
The potential breach notification system requires that when there is an objectively high likelihood of a data breach, affected individuals must be notified within 72 hours. Applicable cases include: unauthorized access to personal information processing systems or devices used by personal information handlers, raising suspicion of a breach but making it difficult to identify specific individuals; and confirmed illegal trading of personal data or other breaches where further exposure of other individuals is anticipated.
The law also mandates ISMS-P (Information Security Management System for Personal Information Protection) certification for key personal information processors in both public and private sectors. However, considering the time required to secure budgets, implementation will begin on July 1 next year. Amendments to the relevant enforcement decree will be separately pursued before the law takes effect.
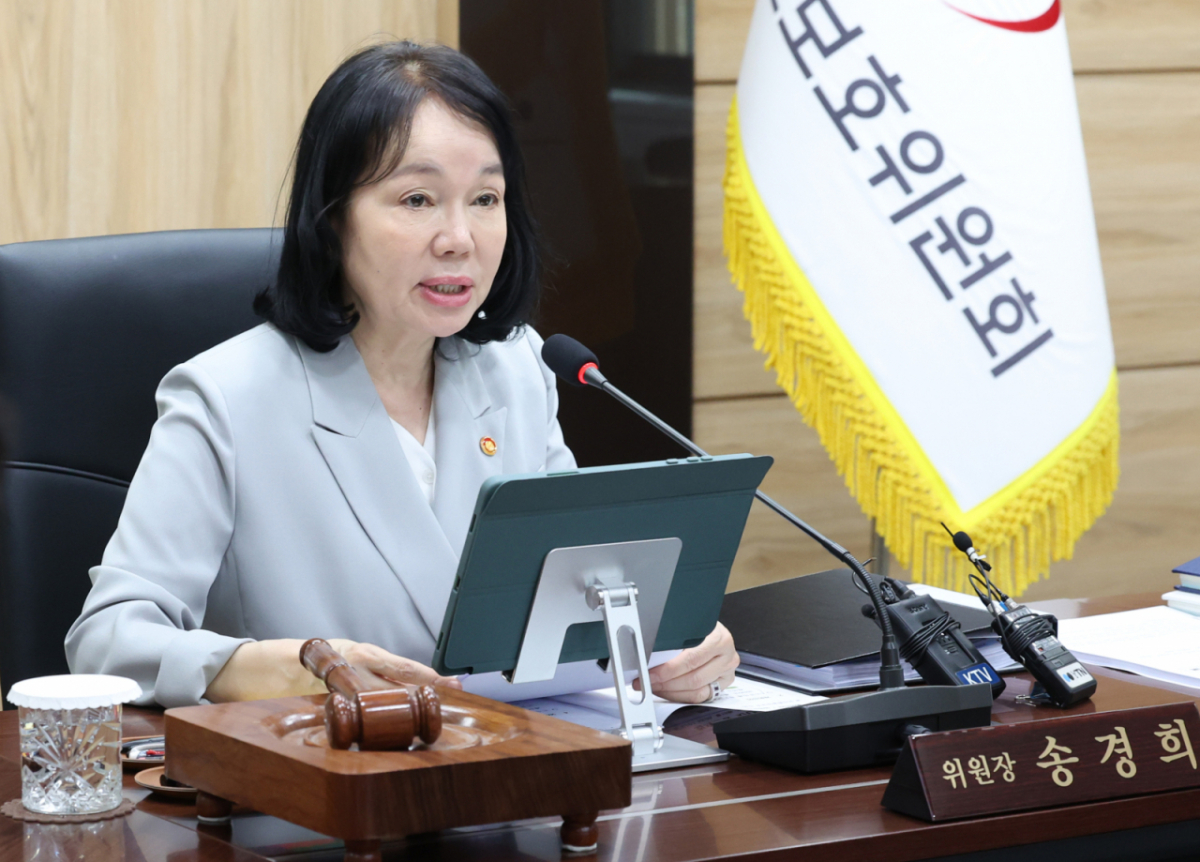
Song Kyung-hee, Chairperson of the Personal Information Protection Commission, stated, "With the implementation of the amended law, we hope that awareness regarding personal data protection will shift from viewing it as a 'cost' to recognizing it as a 'proactive investment' aimed at building trust and expanding corporate benefits."

 in TECH
