

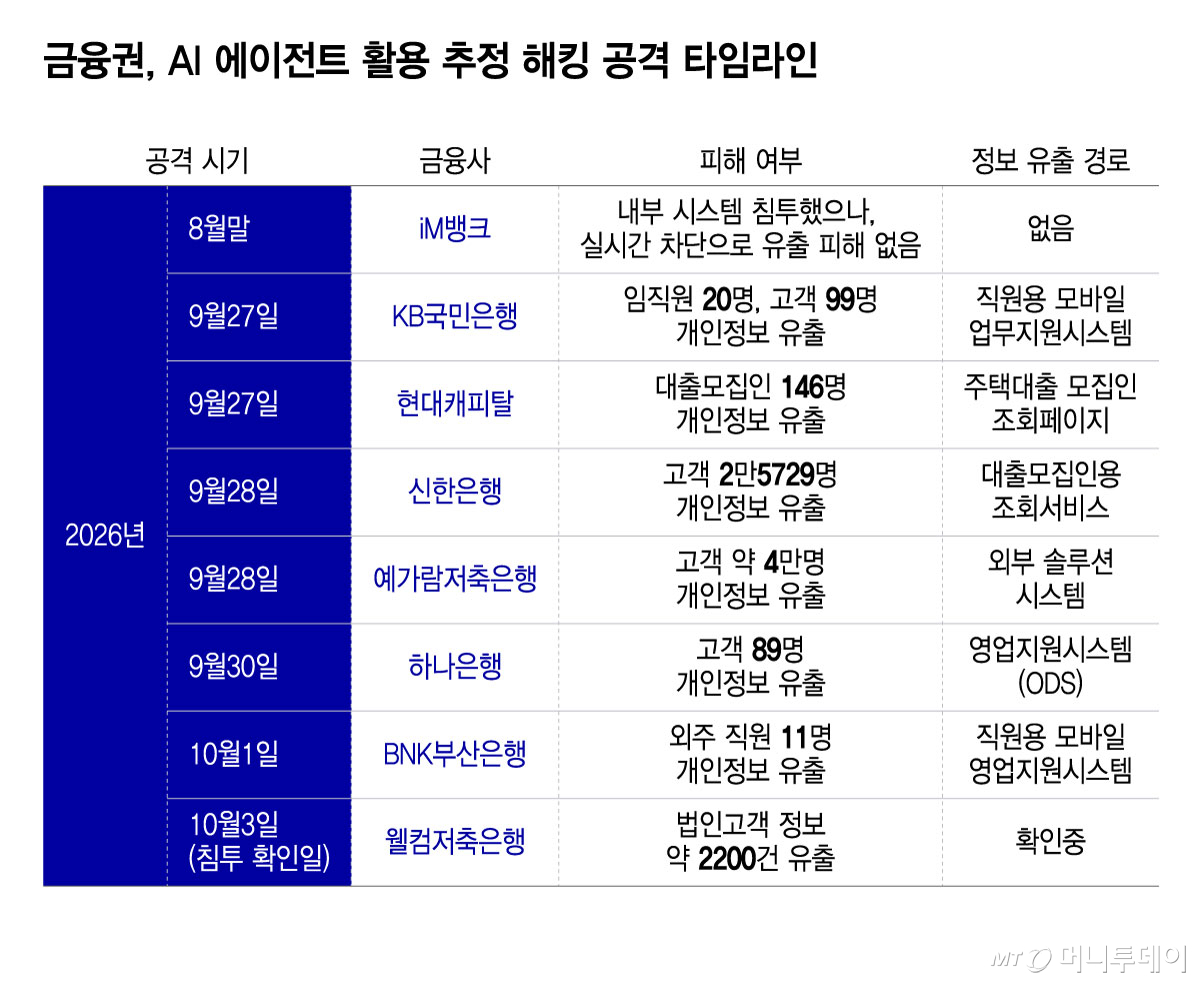
It has been confirmed that a suspected artificial intelligence (AI) hacking attack recently sweeping through the financial sector also occurred just one month ago. In late August, iM Bank detected an intrusion into its internal systems but managed to prevent a data breach through real-time response measures. This incident unfolded after financial regulators had demanded high-level AI-based vulnerability assessments from 10 financial companies targeted for network segregation regulation relaxation, and even after actual attack cases had emerged. Criticism is growing that complacency and inadequate responses within the financial sector were primary causes of this breach.
According to industry sources on the 6th, iM Bank, a commercial bank, detected in late August that external hackers had penetrated its internal systems. While the suspected AI agent attacks and IP (Internet Protocol) addresses involved in recent incidents at seven financial companies differed from those targeting iM Bank, both were similar in their use of AI for hacking purposes. iM Bank immediately shared attack information with the Financial Security Institute and launched joint response efforts to block further intrusions and data leaks.
Following this, iM Bank took follow-up measures, including analyzing the attack path and vulnerabilities at the time and enhancing its security level. As a result, although suspected AI hacking attacks continued to target the financial sector recently, no signs of intrusion were found at iM Bank. It is analyzed that experiencing a similar attack one month earlier and patching vulnerabilities had a decisive impact in preventing actual damage.
In contrast, unlike iM Bank, KB Kookmin Bank, Shinhan Bank, Hana Bank, BNK Busan Bank, and others were helpless against suspected AI agent attacks at the end of last month, resulting in the leakage of customers’ personal credit information.
Notably, when financial regulators lifted network segregation regulations in June, they required 10 financial companies that received non-objection letters to conduct AI-based vulnerability testing. However, it was confirmed that a significant number of these financial companies responded lukewarmly. Financial regulators had initially mandated that the 10th financial companies conduct vulnerability tests utilizing advanced AI by the end of July.
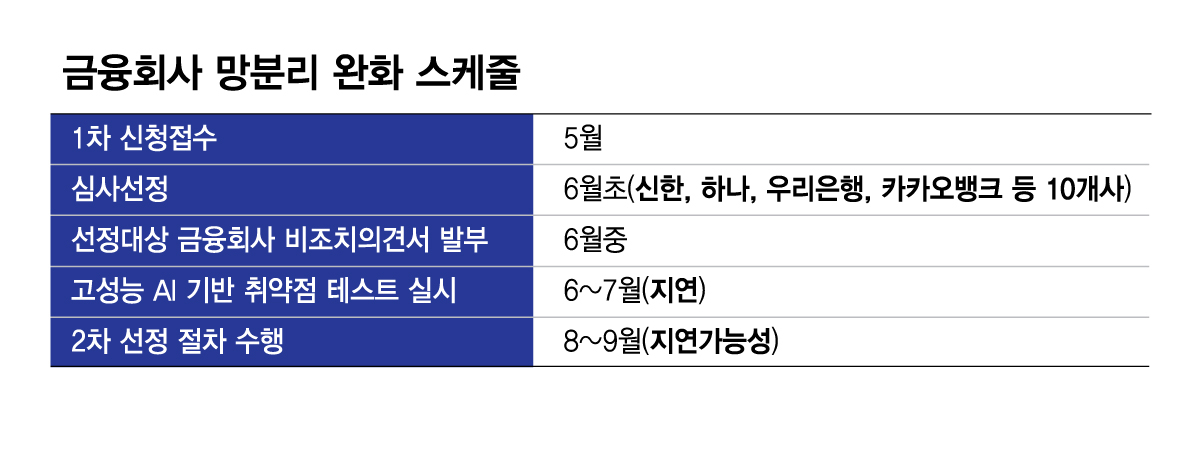
Unlike other financial institutions, these banks, which received exemptions from network segregation regulations, were granted authority for the first time to test internal vulnerabilities using external high-performance AI, such as by contracting with “Amazon Bedrock,” an enterprise-grade safety management generative AI service. Conducting proper vulnerability tests requires a large number of tokens, necessitating substantial cost investment. Furthermore, even when vulnerabilities are discovered, there is often insufficient security personnel available to address them immediately, leading companies to postpone the tests.
Ultimately, financial regulators demanded results from the vulnerability tests last month. Although regulators initially planned to share the vulnerability assessment results from the 10th financial companies with other entities targeted for the second phase of network segregation relaxation, this plan could not proceed as intended. Amid this gap, data breach incidents occurred at Shinhan Bank and Hana Bank, which were part of the first phase of network segregation relaxation.
A source in the financial sector pointed out, “Even if the vulnerability tests did not fully cover attacks on the ‘perimeter’ targeted by this AI hacking incident, the fact that opportunities to inspect main programs using AI were missed clearly reveals the complacent security awareness of financial companies.” The source added, “Taking this crisis as an opportunity, proper AI-based vulnerability assessments must be conducted, even if it requires additional investment in personnel and costs.”

 in FINANCE

