

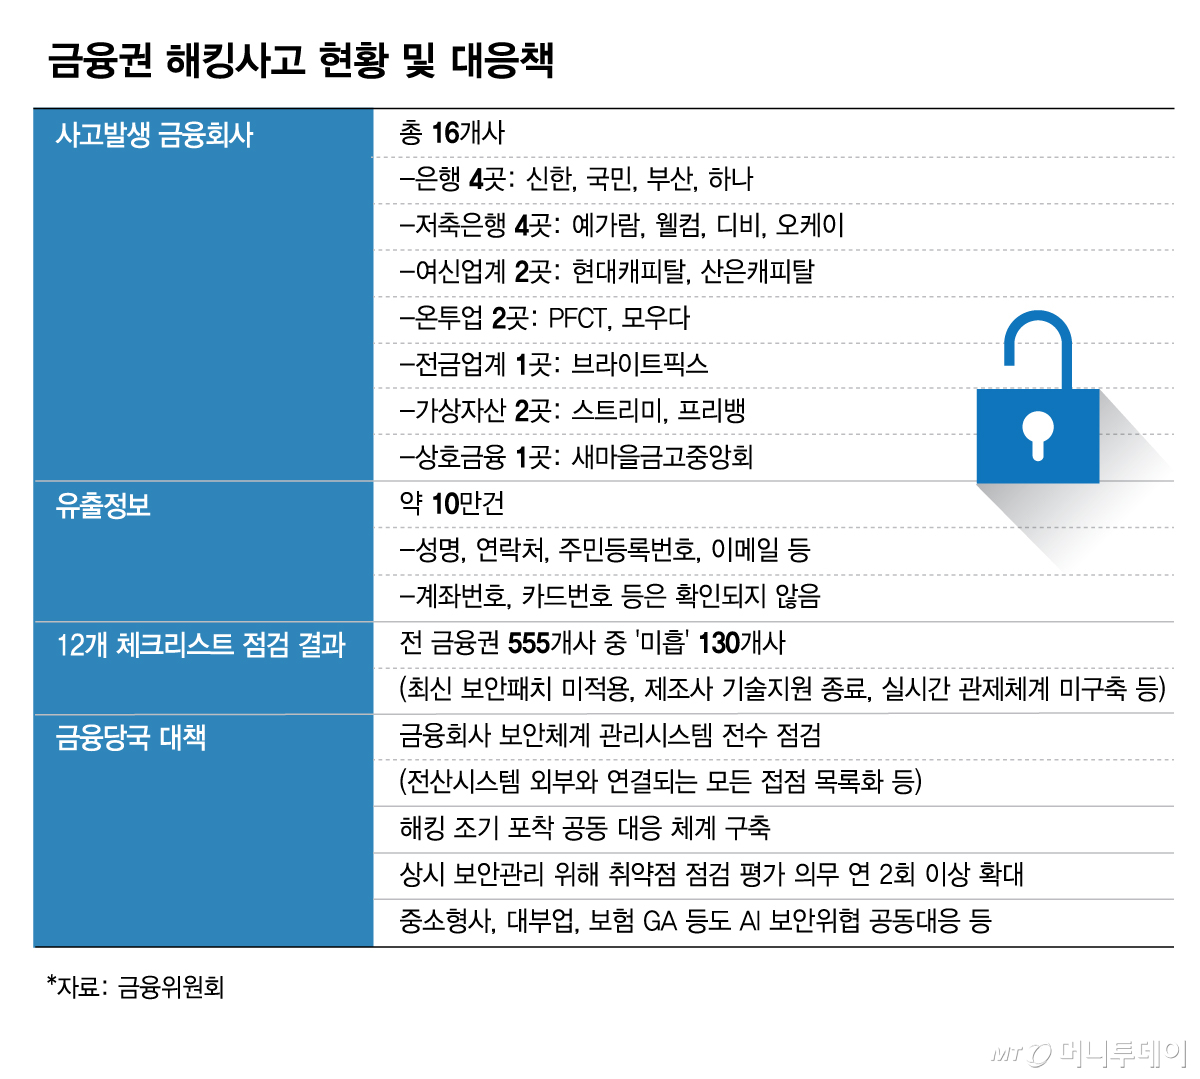
The number of financial companies that suffered a hacking incident, presumed to be an attack by an AI (artificial intelligence) agent, has been identified as 16, far more than the initially reported seven. The leaked information, including resident registration numbers, also reached approximately 100,000 records.
A security checklist review of a total of 555 companies in the financial sector revealed deficiencies at 130 firms. The financial authorities have announced fundamental improvement measures, including a comprehensive inspection of security systems and management frameworks, as well as expanding vulnerability inspections and evaluations from once a year to twice a year or more.
Information leakage of 100,000 records across 16 financial institutions.. Widespread hacking incidents
The Financial Services Commission held its second emergency response meeting on the 14th, chaired by Secretary-General Shin Jin-chang, with relevant institutional investors including the Financial Supervisory Service, the Financial Security Institute, the Ministry of Science and ICT, the Ministry of the Interior and Safety, the Personal Information Protection Commission, and the National Police Agency.
Following an investigation into security breaches across the entire financial sector after the hacking incident at Shinhan Bank at the end of last month, the financial authorities identified information leakage due to hacking at a total of 16 financial companies. Incidents occurred across the board, including banks, savings banks, mutual finance, credit card and specialized lending businesses, electronic finance, online investment-linked services, and virtual asset operators.
Specifically: △ In the banking sector, four institutions were affected: Shinhan, KB Kookmin, Busan, and Hana Bank. △ In the savings bank sector, four firms were involved: Yega람, Welcome, DB, and OK. △ In the specialized credit industry, two firms were affected: Hyundai Capital and Industrial Bank of Korea Capital. Additionally, △ in the online investment-linked business, two firms—PFCT and Mouda—and △ in the electronic finance (one firm) and virtual asset (two firms) sectors, incidents occurred at Bright Pick, Streamy, and Praban, respectively. In the mutual finance sector, one incident occurred at the Saemaul Geumgo Central Association.
The Financial Services Commission stated that since financial companies are currently verifying whether breaches have occurred based on shared IP addresses and other data, the number of affected financial institutions may increase further.
The scale of information leakage in the financial sector confirmed so far is approximately 100,000 records, including names, contact details, resident registration numbers, and email addresses. While the scale of damage has increased compared to initial reports, the Financial Services Commission explained that no leakage of information posing a direct risk of unauthorized transactions, such as account passwords or card numbers, has been confirmed.
The Financial Services Commission announced that for financial companies where incidents have been reported, it has taken measures to prevent further breaches, including blocking attack IPs, applying security patches, and suspending related services. Additionally, the Financial Supervisory Service and the Financial Security Institute are thoroughly investigating the relevance of each case, whether the same entity is responsible, and the possibility of AI hacking by quickly identifying breach paths and attack methods based on on-site investigations.
130 out of 555 companies rated 'deficient' in checklist review.. Expansion to comprehensive security system inspection and at least twice-yearly vulnerability checks
A 12-item checklist review conducted through the 8th across 555 financial sector companies found that a total of 425 firms submitted 'appropriate' results, while 130 firms reported 'deficiencies.' Most of the companies with deficiencies were found to need improvements in one or two inspection items related to security patches and monitoring systems. A relatively large number of deficiencies were found in the electronic finance and online investment-linked sectors, which have weaker security capabilities.
Specifically, reports mainly included: △ failure to apply the latest security patches; △ inadequate management of systems with End-of-Support (EOS) from manufacturers; △ lack of a real-time (24-hour) monitoring system; and △ inadequate attack surface management (such as missing authentication and authorization for external-facing systems, and failure to implement enhanced authentication procedures (MFA) for critical services). It was explained that the relevant companies are immediately implementing measures to address these deficiencies.
The Financial Services Commission will pursue fundamental institutional reforms to structurally and systematically prevent the occurrence of vulnerabilities discovered during checklist reviews. First, it will promote a comprehensive inspection of financial companies' security systems and management frameworks. This involves listing and updating all points where computer systems connect to external networks, and clearly defining and strictly managing authentication and access control permissions for these external connection points. The commission also plans to clarify the reporting lines and scope of responsibility for the operation and management of security systems, including external connection point management, involving CEOs (Chief Executive Officers), CISOs (Chief Information Security Officers), and CIOs (Chief Investment Officers).
A joint response system will also be established to detect hacking early. Hacking threat information identified by the Financial Supervisory Service and the Financial Security Institute is rapidly disseminated across the financial sector through integrated monitoring systems such as FIRST. The system will be improved so that threat information independently identified by financial companies is also shared via the integrated monitoring system. Efforts are also underway to build an AI-based vulnerability inspection infrastructure capable of detecting vulnerabilities in externally exposed assets, internal source code, and mobile apps from an attacker's perspective.
In particular, vulnerability inspections and evaluations, which are currently required once a year under relevant laws (twice a year for external homepages), will be expanded to twice a year or more, starting with large financial institutions. Critical external connection points must be included in mandatory inspection targets. For sectors that struggle to respond to AI security threats, such as small and medium-sized firms, loan businesses, and insurance agencies (GAs), plans are being made to establish a joint security-related system.
Shin Jin-chang (Director) stated, "It is extremely painful that cases have been found where basic standards were not upheld by financial companies, despite repeated orders for comprehensive inspections and strengthened management following various incidents such as the Lotte Card information leak and the US Toss shock." He added, "We will do our utmost to ensure a thorough re-inspection of the entire security system and fundamental institutional reforms, including attack surface management such as external connection points and authentication management at financial companies, as well as securing accountability through the security monitoring framework across the financial sector and by CEOs and boards of directors, using this incident as an opportunity."
He also emphasized, "In preparation for expanding AI security threats, we will more meticulously and swiftly pursue institutional reforms, including relaxing network segregation regulations, to establish a security system that 'defends against AI attacks with AI.'"

 in FINANCE
