

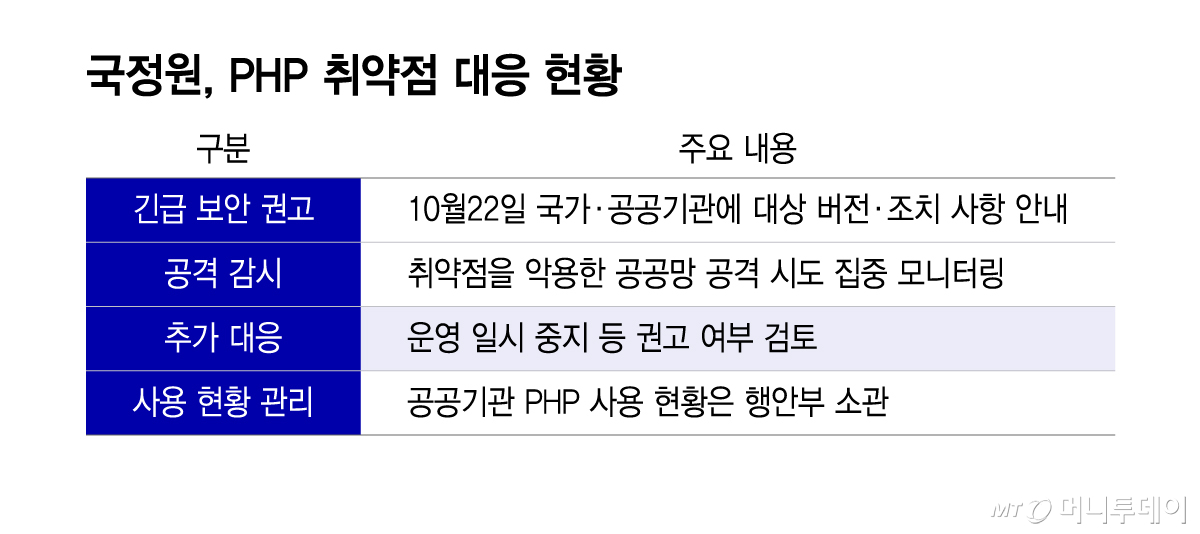
The National Intelligence Service (NIS) is considering a plan to recommend that national and public institutional investors temporarily suspend system operations in response to PHP security vulnerabilities.
With a significant number of domestic PHP servers using older versions that are difficult to patch, the NIS has moved beyond merely urging patches to also reviewing additional measures that could impact the operation of public systems.
On the 27th, the NIS said in response to an inquiry from Money Today, “We are reviewing whether to issue recommendations such as temporary suspension of operations, taking into comprehensive consideration the threat situation.” This means they will recommend temporarily halting public systems if necessary.
If a public system stops operating, it will affect the work or services that use that system. However, this is interpreted as an effort to prepare for the greater risk of public network intrusion that could occur while security measures are delayed.
Previously, on the 22nd, the NIS urgently distributed a security advisory to national and public institutional investors, detailing target versions and required actions. It is guiding each institutional investor to apply patches promptly and is intensively monitoring cyberattack attempts targeting national and public institutional investor computer networks that exploit this vulnerability.
South Korea has a high proportion of users on older versions, which is a factor making security response difficult. According to an analysis by global security firm Malwarebytes, 89% of the 56,423 domestic PHP servers with version information identified via the Shodan internet search engine use PHP 8.1 or lower. This is 15.5 percentage points higher than the global average of 73.5%.
PHP is a programming language widely used for website development and other purposes. Switching from older versions to the latest version can cause compatibility issues, such as existing homepage functions not working properly. This means that even if an organization knows an update is needed, it may be difficult to apply immediately.
The Ministry of Science and ICT and KISA also urged updates and checks for signs of intrusion in their “PHP2Shell Security Vulnerability FAQ” distributed on the 26th. They advised implementing temporary security measures if immediate patching is difficult, and considering temporary suspension of homepage operations if necessary measures are challenging to implement.

 in TECH
