
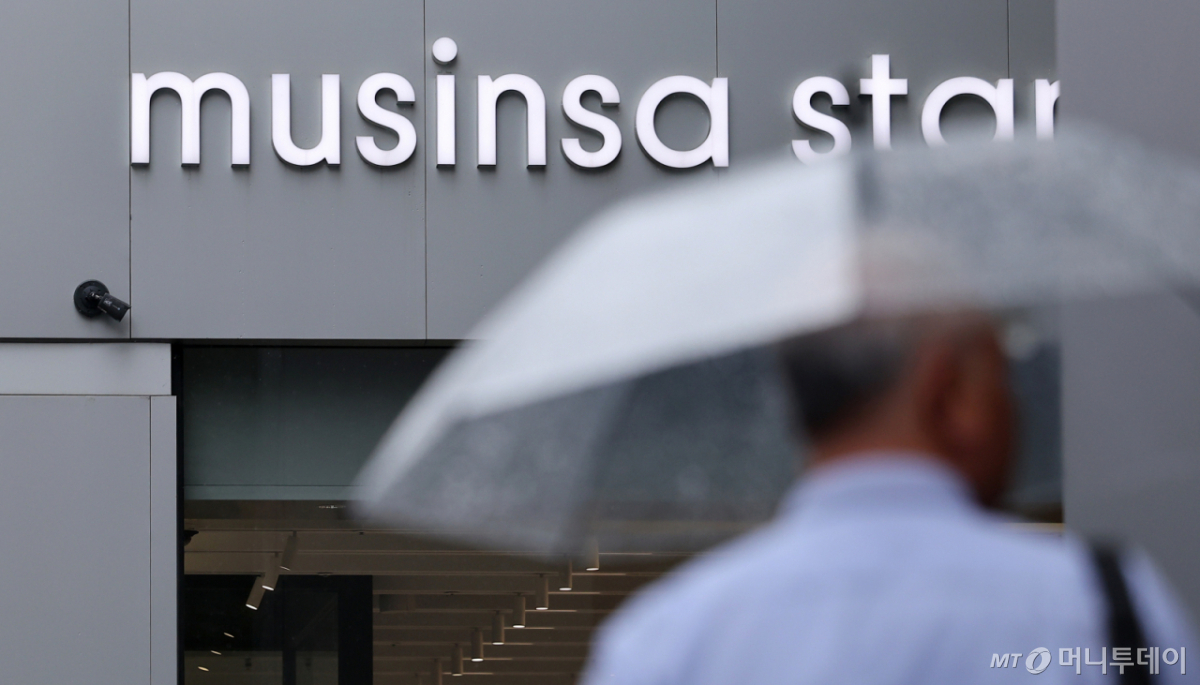
An additional 36,000 cases of personal information infringement (hacking) that occurred at fashion platform company 'Musinsa' in August have been confirmed. Notably, order information was included. When added to the approximately 160,000 cases reported by Musinsa, a total of about 196,000 customers' personal information is estimated to have been leaked.
According to recent cases of personal information infringement submitted by the Personal Information Protection Commission to the office of Lee Jeong-heon, a member of the Democratic Party of Korea, on the 29th, Musinsa reported incidents involving members' order and review information, as well as personal information of warehouse and store staff to authorities on the 16th. This is a separate case from the damage details reported during the personal information infringement incident notification that occurred on the 28th of last month.
The additionally confirmed leaked information includes 32,159 cases containing customer names, email addresses, mobile phone numbers, addresses, delivery memos, tracking information, and order information including exchange-return details. In addition, 103 cases of order information without exchange-return details were found to be leaked, along with 3,999 cases of review information including order numbers, emails, reviewer names, review image URLs (internet addresses), and review registration/modification timestamps. It was also revealed that personal information of Musinsa warehouse and store staff, such as names and mobile phone numbers, totaling 11 cases, had been leaked.
Previously, the number of customer personal information leaks reported by Musinsa to authorities on the 28th of last month and the 3rd of this month totaled 159,852 cases. This includes 138,841 cases of simple name leakage and 21,011 cases of personal information leakage containing names, email addresses, mobile phone numbers, delivery information, etc. When adding the customer personal information leak cases reported on the 16th of this month, the total scale of Musinsa's personal information damage reaches 196,113 cases. In addition to customer personal information, the scale of leaked personal information for Musinsa and partner company employees was also estimated at a total of 35,966 cases.
This personal information leak incident raises concerns about secondary damage spread because it includes relatively sensitive personal information such as products ordered by members through the Musinsa website, contact details, delivery information, exchange-return information, and reviews. Even if hackers do not directly use the leaked information for fraudulent payments, they could exploit payment and refund information for secondary crimes such as phishing, smishing, and vishing.
The Personal Information Protection Commission explained that it "ordered improvements to member order information and API (Application Programming Interface) vulnerabilities, measures against OTP (One-Time Password) authentication vulnerabilities, and operation of a damage relief reception window," and added that they "instructed Musinsa to warn users about spam and phishing attempts impersonating Musinsa or other companies and public institutions."
Lee Jeong-heon (Rep.) stated, "Personal information leak incidents continue to occur in large-scale platforms trusted by the public," and emphasized, "Companies should not only focus on collecting customer information but also bear equal responsibility for protecting it." He further stressed, "Since order, exchange, and return information have been leaked, swift measures are needed to prevent secondary damage to users. During this national audit, we will seriously question the government's management and supervision practices as well as corporate responsibilities for personal information protection."
 in TECH
