
'Maximum administrative fine of 10% of sales' vs 'reduction rate exceeding 80%'.
The Personal Information Protection Act, which takes effect from the 11th, has strengthened both the 'carrot' and the 'stick'. The maximum administrative fine has been raised from 3% to 10% of sales. The reduction rate can reach up to 80% in theory: up to 40% for preventive measures taken in advance and up to 40% for swift actions after a data breach. The intent is to encourage the establishment of a substantive protection system beyond formalistic security investments.
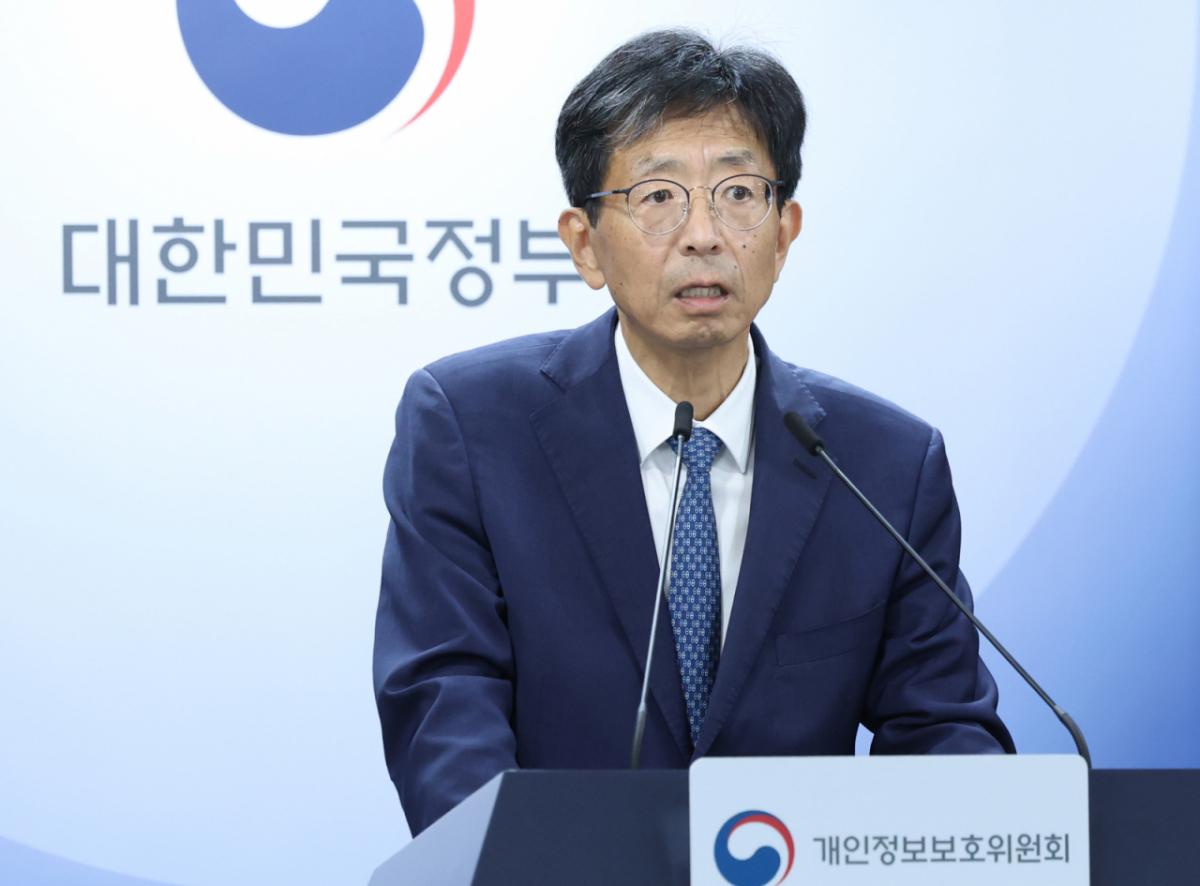
The problem is that, with the enforcement date just one day away, no specific numerical criteria have been provided. Yang Cheong-sam, Secretary-General of the Personal Information Protection Commission, said at a briefing held on the 10th at the Seoul Government Complex in Jongno-gu, Seoul: "There were concerns that incentives for reducing administrative fines should be linked to concrete figures such as security investment amounts, but this is currently difficult."
The Secretary-General cited reasons including industry-specific characteristics and the gap between investment scale and actual security levels. First, he argued that it is difficult to establish consistent standards because security investment amounts vary widely depending on whether the entity responsible for a personal data breach is a public institution or a private company, and what industry it belongs to. He added: "The Ministry of Science and ICT plans to expand the scope of mandatory information protection disclosures starting next year, so indicators such as average, maximum, and minimum values by industry are expected to accumulate. Until then, we will make decisions by comprehensively considering both qualitative and quantitative factors."
He also presented the view that establishing a personal data protection system is just as important as the investment amount. The Secretary-General stated: "Huge security investments do not guarantee the excellence of a company's or institution's personal data management system. Investment scale, leadership commitment, and overall management systems are more important." In fact, large corporations that suffered major personal data breaches last year had the highest levels of personal data protection investment in their industries but still failed to prevent hacking.
Instead, the Personal Information Protection Commission has proposed criteria including: identification of personal data assets; risk assessment at each stage of personal data processing; establishment of an appropriate protection system; authority and role of the Chief Privacy Officer (CPO); reporting cycles to the CEO; and safety measures exceeding the levels required by law. Under the revised Personal Information Protection Act, a reduction of up to 40% will be applied if the protection system is strengthened through prior investment, and another up to 40% for swift response after an incident.
The security industry has expressed both concerns and expectations. There are worries that companies experiencing data breaches may attempt to cover them up to avoid administrative fines. Another anticipated side effect is increased bargaining power for hackers. In response, the Personal Information Protection Commission is preparing a whistleblower reward system targeting companies that conceal breaches. Under next year's budget proposal, 9.4 billion won has been allocated. New penalties will also be introduced for hiding or destroying evidence related to data breach incidents. However, both measures have not yet been formally proposed as bills.
Even before the enforcement of the revised law, the total annual administrative fines were rising sharply. According to the Personal Information Protection Commission, the total amount of administrative fines for personal data breaches by year is as follows: 2020: 6.8 billion won; 2021: 8.2 billion won; 2022: 101.8 billion won; 2023: 23.2 billion won; 2024: 61.2 billion won; 2025: 167.8 billion won; and as of August 2026: 758.9 billion won. These figures exclude fixed penalties (fines).
Conversely, there is also expectation that higher reduction rates will lead to increased preventive investment. An industry official stated: "From a corporate perspective, efforts made to strengthen security will be felt as having tangible effects in reducing administrative fines. With cyberattacks becoming more sophisticated due to advances in AI and other technologies, even well-prepared organizations can be breached; thus, the reduction rate will serve as an effective carrot."
 in TECH
