
Recently, seven domestic financial institutional investors were left helpless in the face of AI-driven hacking attacks. A key characteristic of these attacks is that they did not employ any groundbreaking new hacking techniques; instead, AI was leveraged to execute existing hacking methods rapidly and on a large scale. It is difficult for humans to stop indiscriminate AI attacks. The security industry is raising its voice, arguing that AI hacking must be defended against with AI, and that if proprietary AI models are unavailable, there is an urgent need to build defensive systems using open-source models.
According to financial authorities on the 5th, this hacking of financial institutional investors did not involve directly seizing databases (DBs); rather, it used a method of mass-querying and scraping customer information from web pages and servers. Given the speed and repetitive nature of the technique, it is estimated that AI tools were utilized.
Traces of “ARTEX,” an AI penetration testing tool released as open source by Chinese-speaking developers, were detected on the attacking IP (Internet Protocol) addresses. This means an AI tool intended for vulnerability assessment was exploited for hacking purposes. ARTEX utilizes large language models (LLMs) to explore and analyze vulnerabilities, and calls upon necessary tools to verify them.
The security industry argues that AI must be introduced into defense systems to prepare for automated AI hacking attacks. They contend that AI should be used to rapidly analyze attack data and identify correlations between different events. Kang Seok-gyun of An Raep (CEO) explained the need for investment in AI technology for hacking defense at a recent press conference, stating, “AI cyberattacks have surpassed the level at which humans can judge and respond, in terms of productivity, speed, and scale.”
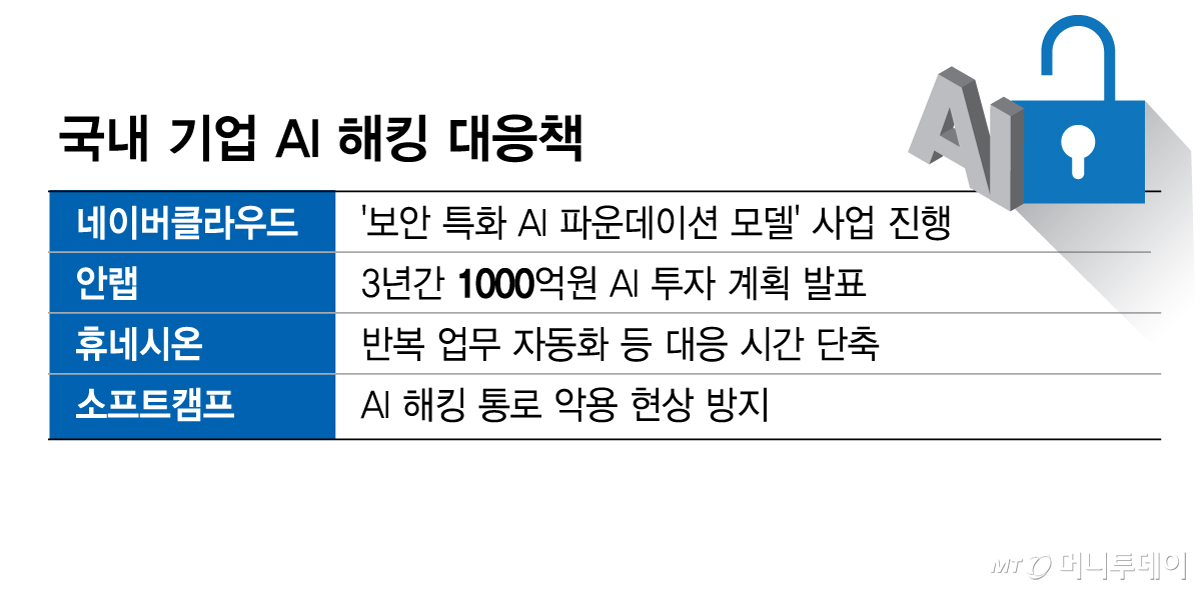
The government is also preparing countermeasures against the risks of AI hacking. Recently, it selected the Naver Cloud consortium for the “Security-Specialized AI Foundation Model” project to build a hacking defense line using proprietary AI. Additionally, it will proceed with the national- and institutional-level AI Cyber Shield Dome project for five years starting next year.
However, it takes time to develop domestic AI models for defense. Consequently, there are calls that immediate response is necessary by utilizing publicly available open-source models. Choi Dae-sun, head of the AI Safety Research Center at Soongsil University, stated, “Simply combining agents with currently public AI models can endow them with powerful offensive capabilities,” and added, “While proprietary AI may be utilized in the long term, existing AI must be applied to respond to immediate AI threats.” He further noted that by layering multi-agents and analytical tools onto “Opus 4.6,” the score on a vulnerability discovery benchmark evaluation (CyberZim) increased significantly from 66.6 points to 91 points.
Domestic security companies are also increasing their AI investments. AhnLab will invest an additional 100 billion won in AI over the next three years, excluding its existing R&D (Research and Development). Secure Systems, a subsidiary of Huneosion, has launched “Secure Orchestra,” an AI-based integrated security platform. The AI automates repetitive human tasks and analyzes priorities to shorten response times. SoftCamp has introduced “ShieldGate,” a web-isolation-based secure remote access service, to prevent the phenomenon of AI being exploited as a hacking channel.
Adhering to existing security principles, such as continuous inspection of externally exposed assets and vulnerabilities, is also important. A source in the security industry said, “It is important to strengthen existing security systems such as multi-factor authentication (MFA), least privilege, and access control, as well as to appropriately manage the AI introduced for defense.”
 in TECH
