
The Ministry of Science and ICT announced that it will invest 50 billion won in budget for SME (small and medium-sized enterprise) security amid the recent all-around spread of AI hacking risks.
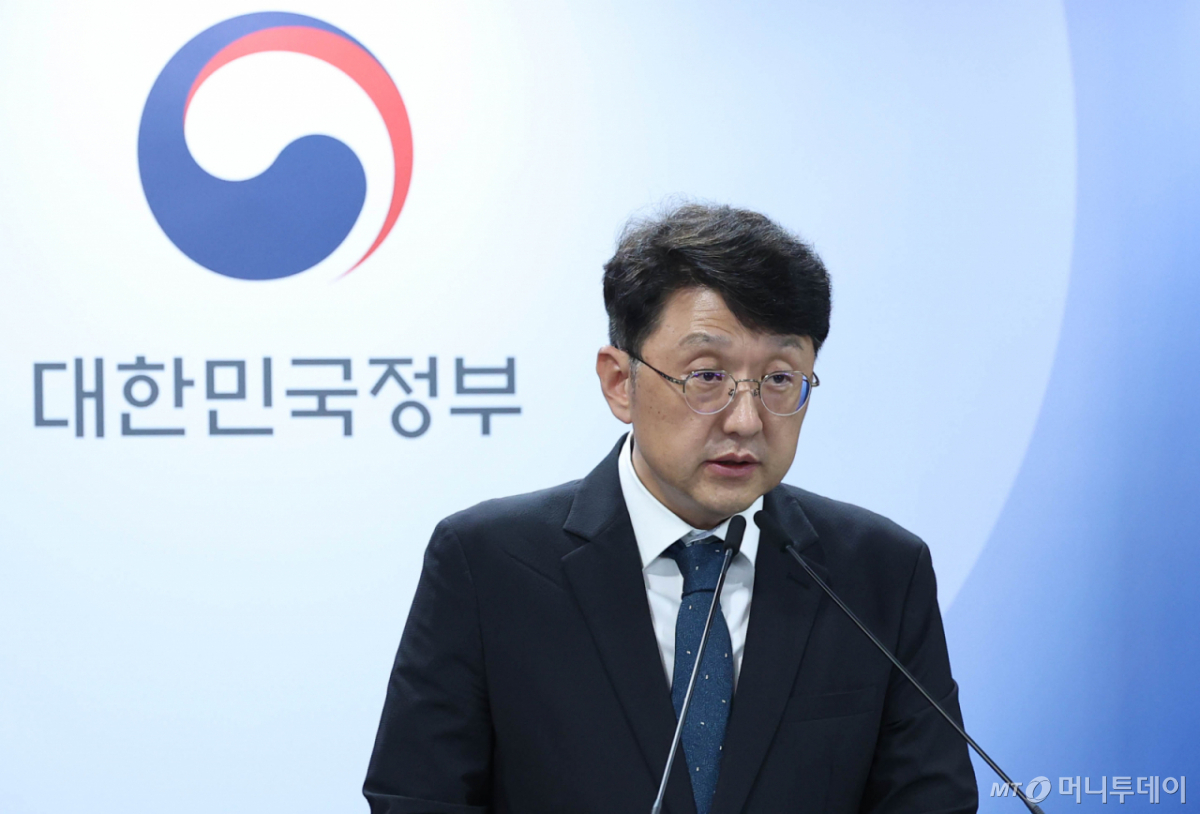
Choi Woo-hyuk, Director of the Information Protection and Network Policy Division at the Ministry of Science and ICT, stated during the National Assembly’s audit of the Ministry of Science and ICT and Korea Communications Commission held on the 15th, “This year, a budget of 3 billion won was allocated for SME security support, assisting over 2,900 companies,” adding, “We have allocated a budget of 50 billion won for the security monitoring service to provide intensive support to SMEs next year, so we ask for your great interest in the budget proposal.”
Amid the recent realization of AI hacking led by the financial sector, there were also criticisms that the government’s security-specialized AI model (Teukpamo) is too late.
In response, Director Choi said, “We have been working on the Teukpamo project since September, so it does feel a bit late,” adding, “Before that, we have been conducting security checks using OpenAI’s G-TAC (Government and institutional investor Trusted Access Program).”
He further announced plans to institutionalize the ‘Vulnerability Disclosure Policy’ (VDP) and the ‘Coordinated Vulnerability Disclosure’ (CVD) project, which allows anyone to participate as a white hacker to find and report security vulnerabilities in companies and public institutional investors.
Director Choi stated, “AI hacking differs from existing hacking in that it is characterized by being executed automatically in very short bursts of time,” adding, “Hackers can attack sites at any time, but if white hackers attack, it becomes an illegal act. To mitigate this, we are currently running a pilot project to allow white hackers to attack and find vulnerabilities so they can be reinforced.”
Meanwhile, the Ministry of Science and ICT and the Korea Internet & Security Agency (KISA) launched the country’s first ‘Security Vulnerability Reporting, Response, and Disclosure System’ (Permanent Security Vulnerability Reporting and Response System) pilot project in May. The project was created to prepare for AI attacks following the ‘MiToss Shock,’ and it also allows white hackers to use AI for hacking within the pilot program. From June to November, white hackers will conduct vulnerability exploration, reporting, and response activities on companies’ homepages or permitted sites as if in a real-world scenario.
 in TECH
