
As hacking attacks have spread from banks to savings banks and capital companies, the financial regulator is set to urgently convene a meeting with the entire financial sector. The gathering will include the financial investment and insurance sectors, where no damage has yet been confirmed, in order to discuss response measures aimed at preventing further incidents.
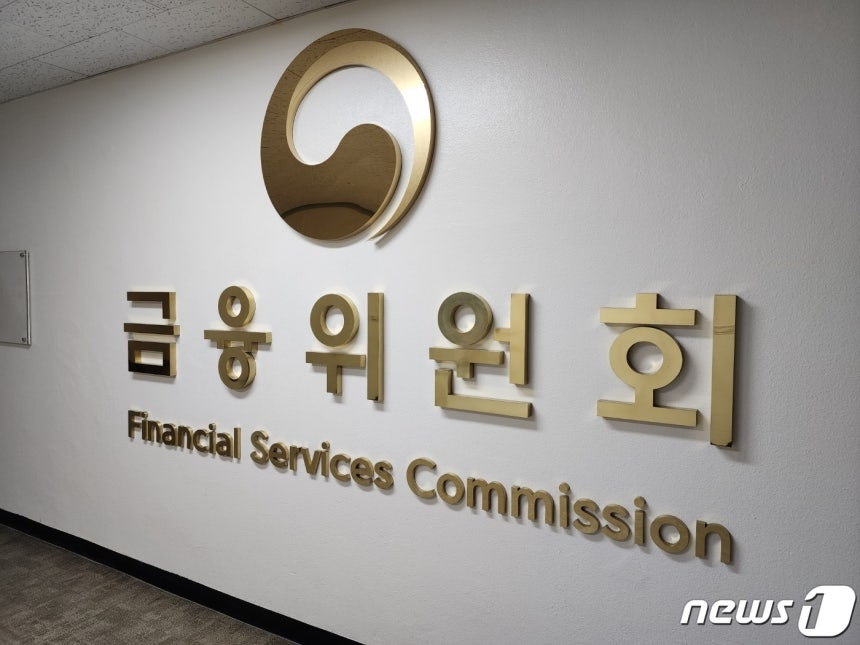
According to industry sources on the 3rd, the Financial Services Commission will hold an all-sector meeting at 2 p.m. on the 4th, chaired by Lee Eui-won, Chairman of the Financial Services Commission, with Lee Chan-jin, Head of the Financial Supervisory Service, also in attendance. The meeting was moved up from its originally scheduled date of the 7th following a series of hacking incidents. Heads of industry associations for banks, financial investment, insurance, cards and capital companies, savings banks, mutual finance, virtual assets, and fintech are expected to attend. Senior executives (CEO-level) from recently affected financial institutions will participate, as will the presidents of KB Kookmin Bank, Shinhan Bank, Hana Bank, and Busan Bank, four banks that have suffered hacking damage.
The meeting aims to share the current status of recent consecutive data breach incidents and prepare for similar attacks. The financial regulator plans to instruct each financial institution to inspect vulnerabilities in its computer systems and observe security precautions.
Recent hacking damage has spread beyond the banking sector to the second-tier financial market. At Yega람 Savings Bank, customer information belonging to approximately 40,000 individuals was leaked due to a hack. Hyundai Capital also experienced an incident involving the leakage of personal information of its home loan solicitors. The day before, consecutive data breach cases were confirmed within the banking sector as well. Woori Bank and NH NongHyup Bank reported no customer information leakage but did experience hacking attempts.
In particular, because this incident occurred not only in core financial systems but also across various computer domains such as business support systems and information inquiry services, the need for comprehensive security inspections across all financial institutions is growing. Although no related damage has yet been confirmed in the financial investment and insurance sectors, the financial regulator plans to share incident cases to help each sector inspect its vulnerabilities and prepare for additional attacks.
 in FINANCE
